Posts
Agentic AI Risk. Simplified.
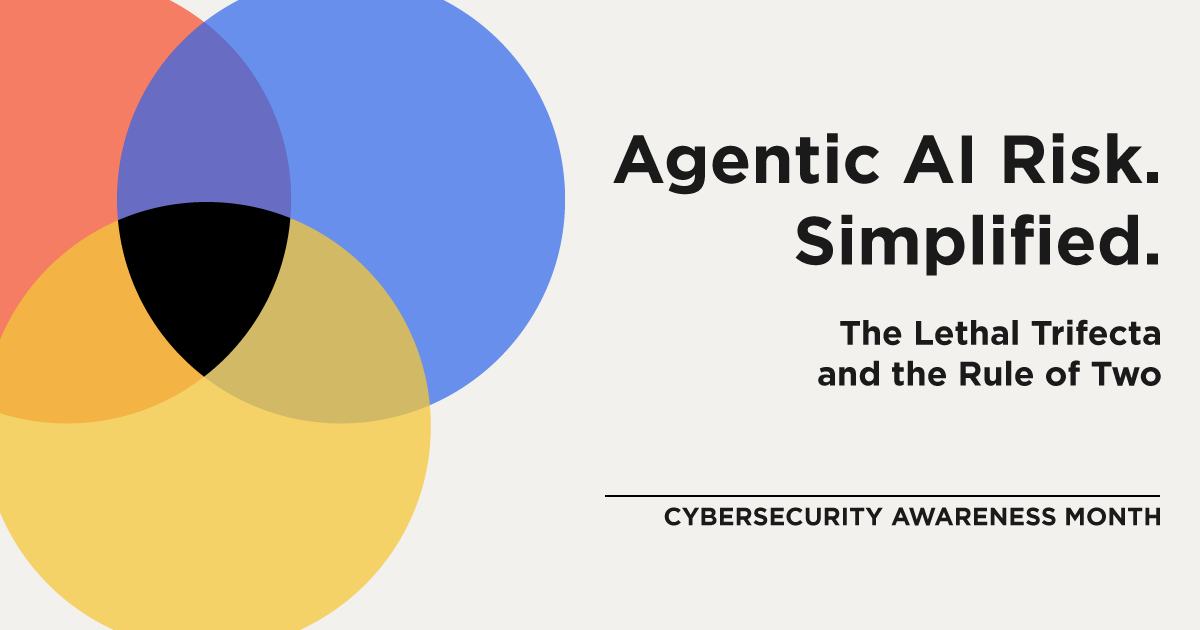
The Lethal Trifecta and the Rule of Two, Simplified for Cybersecurity Awareness Month.
Nicholas Molina
October 5, 2026
This intentionally simplified piece distills a key risk of agentic AI for Cybersecurity Awareness Month.
Use Agentic AI Safely: Beware the Lethal Trifecta.
The fundamental issue with agentic AI, or AI that can act on your behalf, is that it cannot reliably distinguish between your instructions and the emails, documents, web pages, and other content that it processes for you. This is what makes prompt injection possible, an attack where malicious instructions embedded in content hijack your agent to do an attacker’s bidding instead of yours.
An AI agent needs three capabilities to do you serious harm, capabilities which you grant. Simon Willison, the researcher who coined the term prompt injection, calls them the lethal trifecta:
- Access to sensitive systems or private data
- Ability to process untrusted content
- Ability to communicate externally or make system changes
Take an agent that can read and send email: trifecta completed. The same agent can read your private emails, read hidden instructions in an inbound email, and reply to an attacker with your confidential information.
Avoid completing the lethal trifecta with the Rule of Two: never give an agent more than two of the three lethal capabilities. In our email scenario, break any one link in the chain by denying the agent’s ability to send email, restricting the agent to only interacting with known trustworthy senders, or limiting it to a special-purpose mailbox that doesn’t contain sensitive data.
But wait, I’m safe if every agent action requires my approval, right? No, this doesn’t hold up in reality. First, if an agent is asking for your approval, it is deciding what to tell you when it asks. Second, when users are habitually prompted to approve agent actions, they tend to get fatigued and start habitually approving them.
Use the Rule of Two to keep your agents working for you.